10 Common Cybersecurity Mistakes Developers Make
Quick Answer: Developers commonly create security risks by hardcoding secrets, trusting user input, skipping authorization checks, using outdated dependencies, misconfiguring applications, mishandling authentication, exposing sensitive data in logs, and treating security as something to fix after development.
Cybersecurity is no longer something developers can leave entirely to a separate security team. Modern applications depend on APIs, third-party packages, cloud services, CI/CD pipelines, databases, containers, and external integrations. A small mistake in any one of those areas can create an opening for attackers.
The good news is that many developer security mistakes are preventable. The first step is recognizing the patterns that repeatedly cause problems.
The OWASP Top 10:2025 identifies broken access control, security misconfiguration, software supply chain failures, cryptographic failures, injection, insecure design, authentication failures, software or data integrity failures, logging and alerting failures, and mishandling of exceptional conditions among the most important web application security risks.
Here are 10 common cybersecurity mistakes developers should avoid.
Hardcoding Passwords, API Keys and Secrets
One of the easiest mistakes to make is putting a password, API key, database credential, private token, or other secret directly into source code.
For example, a developer might place an API key inside a JavaScript file because it makes testing quick. The problem appears when that code reaches a public repository, shared development environment, application bundle, or backup.
Hardcoded credentials can be difficult to remove completely because they may remain in Git history even after the developer deletes them from the latest version.
How to avoid it
Use environment variables or an appropriate secrets-management system instead of putting credentials directly into application code. Developers should also scan repositories for accidentally committed secrets and immediately rotate credentials that have been exposed.
This is particularly important as modern development environments increasingly depend on automated tools, CI/CD systems, package registries, and AI-assisted coding workflows.
Trusting User Input
Applications should assume that information coming from users is untrusted.
Search boxes, login forms, URL parameters, file uploads, API requests, and other inputs can all be manipulated. When developers use that information without appropriate validation or safe handling, they can create vulnerabilities such as SQL injection, cross-site scripting, command injection, and other injection attacks.
OWASP continues to identify injection as a major application security risk and recommends validating and sanitizing untrusted input at appropriate application boundaries.
How to avoid it
Validate input on the server, use parameterized queries, apply context-appropriate output encoding, and avoid constructing commands from raw user-controlled strings.
Client-side validation can improve the user experience, but it should never be treated as the primary security control.
Checking Authentication but Forgetting Authorization
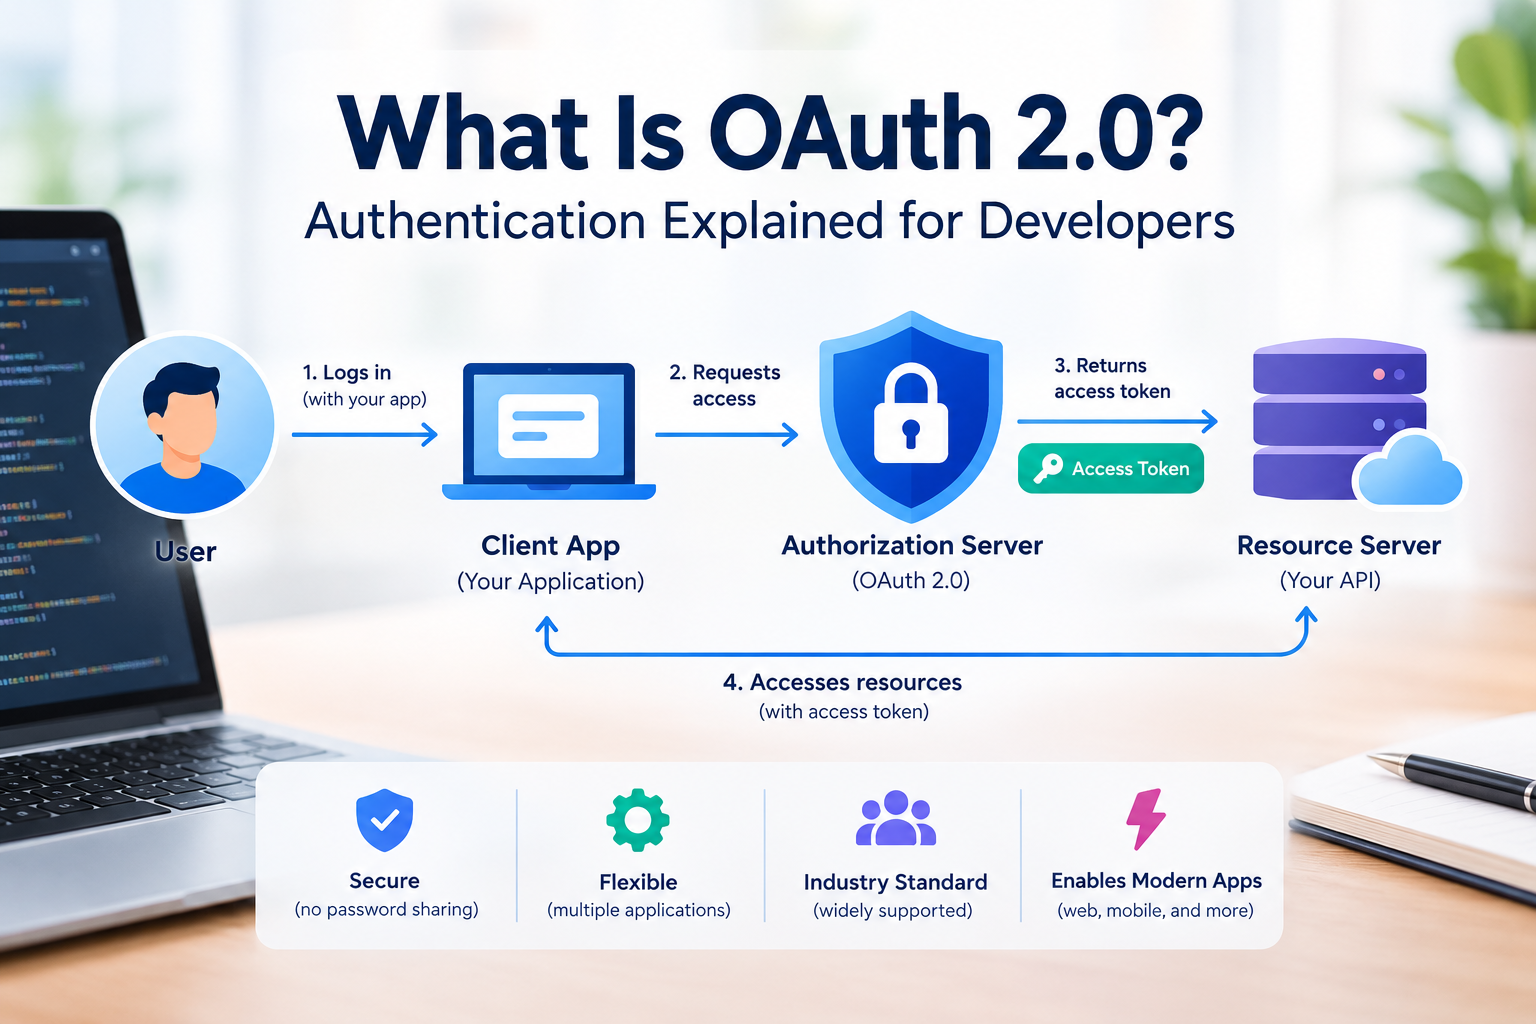
Authentication answers one question: Who are you?
Authorization answers another: What are you allowed to do?
Developers sometimes verify that a user is logged in but fail to check whether that user actually has permission to access a particular record, administrative function, account, or API endpoint.
For example, a user might change an ID in a URL and gain access to another customer's information if the server does not perform an ownership check.
This falls under the broader problem of broken access control, which remains A01 in the OWASP Top 10:2025.
How to avoid it
Perform authorization checks on the server for every sensitive operation. Do not assume that hiding a button in the frontend prevents a user from calling the underlying API.
Use least-privilege permissions and explicitly define what each role or account can access.
Using Outdated or Untrusted Dependencies
Modern developers rarely build applications entirely from scratch. Frameworks, libraries, packages, plugins, containers, APIs, and development tools are part of almost every software project.
That convenience also creates a supply-chain risk.
An outdated library may contain a known vulnerability. An abandoned package may no longer receive security updates. A compromised package can potentially introduce malicious code into an otherwise legitimate application.
OWASP's 2025 update moved Software Supply Chain Failures to A03 and expanded the category beyond traditional vulnerable components to include broader problems involving dependencies, development tools, CI/CD systems, repositories, and artifacts.
How to avoid it
Keep dependencies inventoried and updated. Remove packages that are unnecessary or unmaintained, monitor vulnerability advisories, use trusted package sources, and review dependency changes before they reach production.
Developers should also remember that transitive dependencies matter. A package you did not directly install can still become part of your application's attack surface.
Leaving Security Until the End of Development
Security is much harder to add after an application's architecture has already been built.
A development team might first create authentication, data flows, APIs, payment functions, and administrative features and only later ask whether the design is secure.
By then, fixing fundamental problems can require major architectural changes.
OWASP's 2025 guidance on insecure design recommends incorporating threat modeling, secure design patterns, security controls, and security-focused tests into the development process rather than treating security as an afterthought.
How to avoid it
Think about security during planning.
Before building a sensitive feature, ask:
What could an attacker control? What data could be exposed? Which users should have access? What happens if an API request is manipulated? What happens if a service becomes unavailable? What is the worst-case result of a successful attack?
These questions can reveal architectural problems before they become expensive to fix.
Misconfiguring Production Systems
A secure application can still become vulnerable because of an insecure configuration.
Common examples include leaving debug mode enabled, using default credentials, exposing administrative interfaces, allowing unnecessary network access, enabling excessive permissions, or returning overly detailed error messages.
Security misconfiguration is A02 in the OWASP Top 10:2025.
How to avoid it
Use secure production configurations and remove development-only features before deployment.
Developers should also review:
Cloud permissions
Database access
Firewall rules
Container configurations
API settings
CORS policies
Error handling
Default accounts
Debugging features
Configuration should be treated as part of the application's security posture, not as an operational detail that can be ignored by developers.
Using Weak Authentication and Session Management
Authentication systems are attractive targets because compromising an account can give an attacker legitimate-looking access to an application.
Common mistakes include weak passwords, ineffective password recovery, poorly protected sessions, excessive login attempts, long-lived tokens, and missing multifactor authentication.
OWASP identifies authentication failures as a major application security category and specifically highlights risks such as credential stuffing, brute-force attacks, weak credentials, session fixation, and improper session invalidation.
How to avoid it
Use established authentication frameworks rather than creating a custom authentication system without a strong reason.
Use MFA where appropriate, protect session tokens, invalidate sessions properly, rate-limit authentication attempts, and never store passwords in plaintext.
Developers should also avoid creating their own cryptographic algorithms or password-hashing schemes.
Logging Sensitive Information
Logs are essential for troubleshooting and detecting attacks, but they can become a security problem when developers log too much information.
Passwords, authentication tokens, API keys, payment information, personal data, and other sensitive values should not casually appear in application logs.
A developer may initially add detailed logging to diagnose a problem and forget to remove it before production.
The OWASP Top 10:2025 specifically includes Security Logging and Alerting Failures as A09.
How to avoid it
Log useful security events without unnecessarily exposing sensitive information.
Monitor events such as repeated failed logins, privilege changes, suspicious access attempts, and important administrative actions. At the same time, establish clear rules about what should never be written to logs.
Security logs should also be protected because an attacker who can modify or delete them may make an intrusion much harder to investigate.
Ignoring CI/CD and Software Integrity
Developers often focus on securing application code while overlooking the systems that build and deploy it.
That can be dangerous.
A compromised repository, build server, package, deployment credential, or CI/CD pipeline can potentially introduce malicious changes into production.
OWASP's 2025 guidance recommends protecting repositories, developer workstations, build servers, CI/CD systems, artifacts, and infrastructure-as-code environments.
How to avoid it
Protect CI/CD credentials, use MFA for important developer accounts, restrict pipeline permissions, review changes to build configurations, and verify the integrity of important artifacts.
Developers should also avoid giving automated systems more privileges than they actually need.
This is increasingly important as organizations automate more of the software development and deployment process.
Handling Errors and Exceptions Poorly
Errors happen in every application. The security problem begins when an application handles them in a way that exposes information or creates unexpected behavior.
A detailed database error might reveal internal table information. A stack trace could expose application paths or implementation details. An improperly handled exception might bypass an important security check or leave an application in an unsafe state.
OWASP's 2025 framework now includes Mishandling of Exceptional Conditions as A10, highlighting the importance of secure failure behavior.
How to avoid it
Applications should fail safely.
Show users a useful but limited error message while recording appropriate diagnostic information securely on the server. Test unexpected conditions instead of testing only the application's normal workflow.
Developers should ask what happens when a database connection fails, a payment request times out, a permission check cannot complete, or an external API returns unexpected data.
Why Developers Should Treat Security as Part of Coding
Many cybersecurity vulnerabilities do not begin with an obviously malicious developer action. They often start with a small shortcut:
A credential is hardcoded for testing.
A dependency is never updated.
An authorization check is assumed rather than verified.
Debugging remains enabled after deployment.
A sensitive value is added to a log.
A CI/CD token receives excessive permissions.
An unusual error condition is never tested.
Individually, these decisions can appear harmless. In a production application, however, they can create opportunities for attackers.
The modern security mindset is therefore less about memorizing a list of vulnerabilities and more about questioning trust at every boundary.
A Simple Security Checklist for Developers
Before deploying an application, developers can use this quick checklist:
| Security Area | Question to Ask |
|---|---|
| Secrets | Are passwords and API keys kept outside the source code? |
| Input | Is untrusted input validated and handled safely? |
| Authorization | Does every sensitive action verify user permissions? |
| Dependencies | Are third-party packages tracked, reviewed, and updated? |
| Authentication | Are passwords, sessions, and tokens properly protected? |
| Configuration | Are production settings properly hardened? |
| Logging | Could application logs expose sensitive information? |
| CI/CD | Are pipelines and deployment credentials properly protected? |
| Errors | Does the application fail safely without revealing sensitive details? |
| Design | Was security considered before implemen |
Final Takeaway
Developers do not need to become full-time security specialists to write safer software. They do, however, need to understand how everyday development decisions can create security weaknesses.
The most important habits are straightforward: protect secrets, validate untrusted input, enforce authorization, maintain dependencies, secure authentication, harden configurations, protect logs, secure CI/CD pipelines, and design for failure.
Following established guidance such as the OWASP Top 10 can give development teams a practical starting point. The current 2025 version is particularly useful because it reflects a broader modern attack surface that includes software supply chains, development infrastructure, application integrity, and operational security.
Security works best when it becomes part of the development process rather than a final inspection before launch.